How do you recover from a ransomware attack? You cut off the infected machines first, then call in help and report it. After that comes the slow part. You find out how the attackers got in and rebuild clean systems. Then you restore your data from backups they couldn’t touch. Paying the ransom doesn’t skip any of that.
The order matters. Restore too early, and you can reinfect everything. Wipe too fast, and you destroy the evidence your insurer and law enforcement need.
The federal Cybersecurity and Infrastructure Security Agency (CISA) lays out the same order in its ransomware guidance, and we’ve stuck close to it. Happening to you right now? Unplug first. Then call your IT provider.
Contain the Attack in the First Hour
Stop the spread. Ransomware moves across a network fast, so every minute a machine stays connected puts more files at risk.
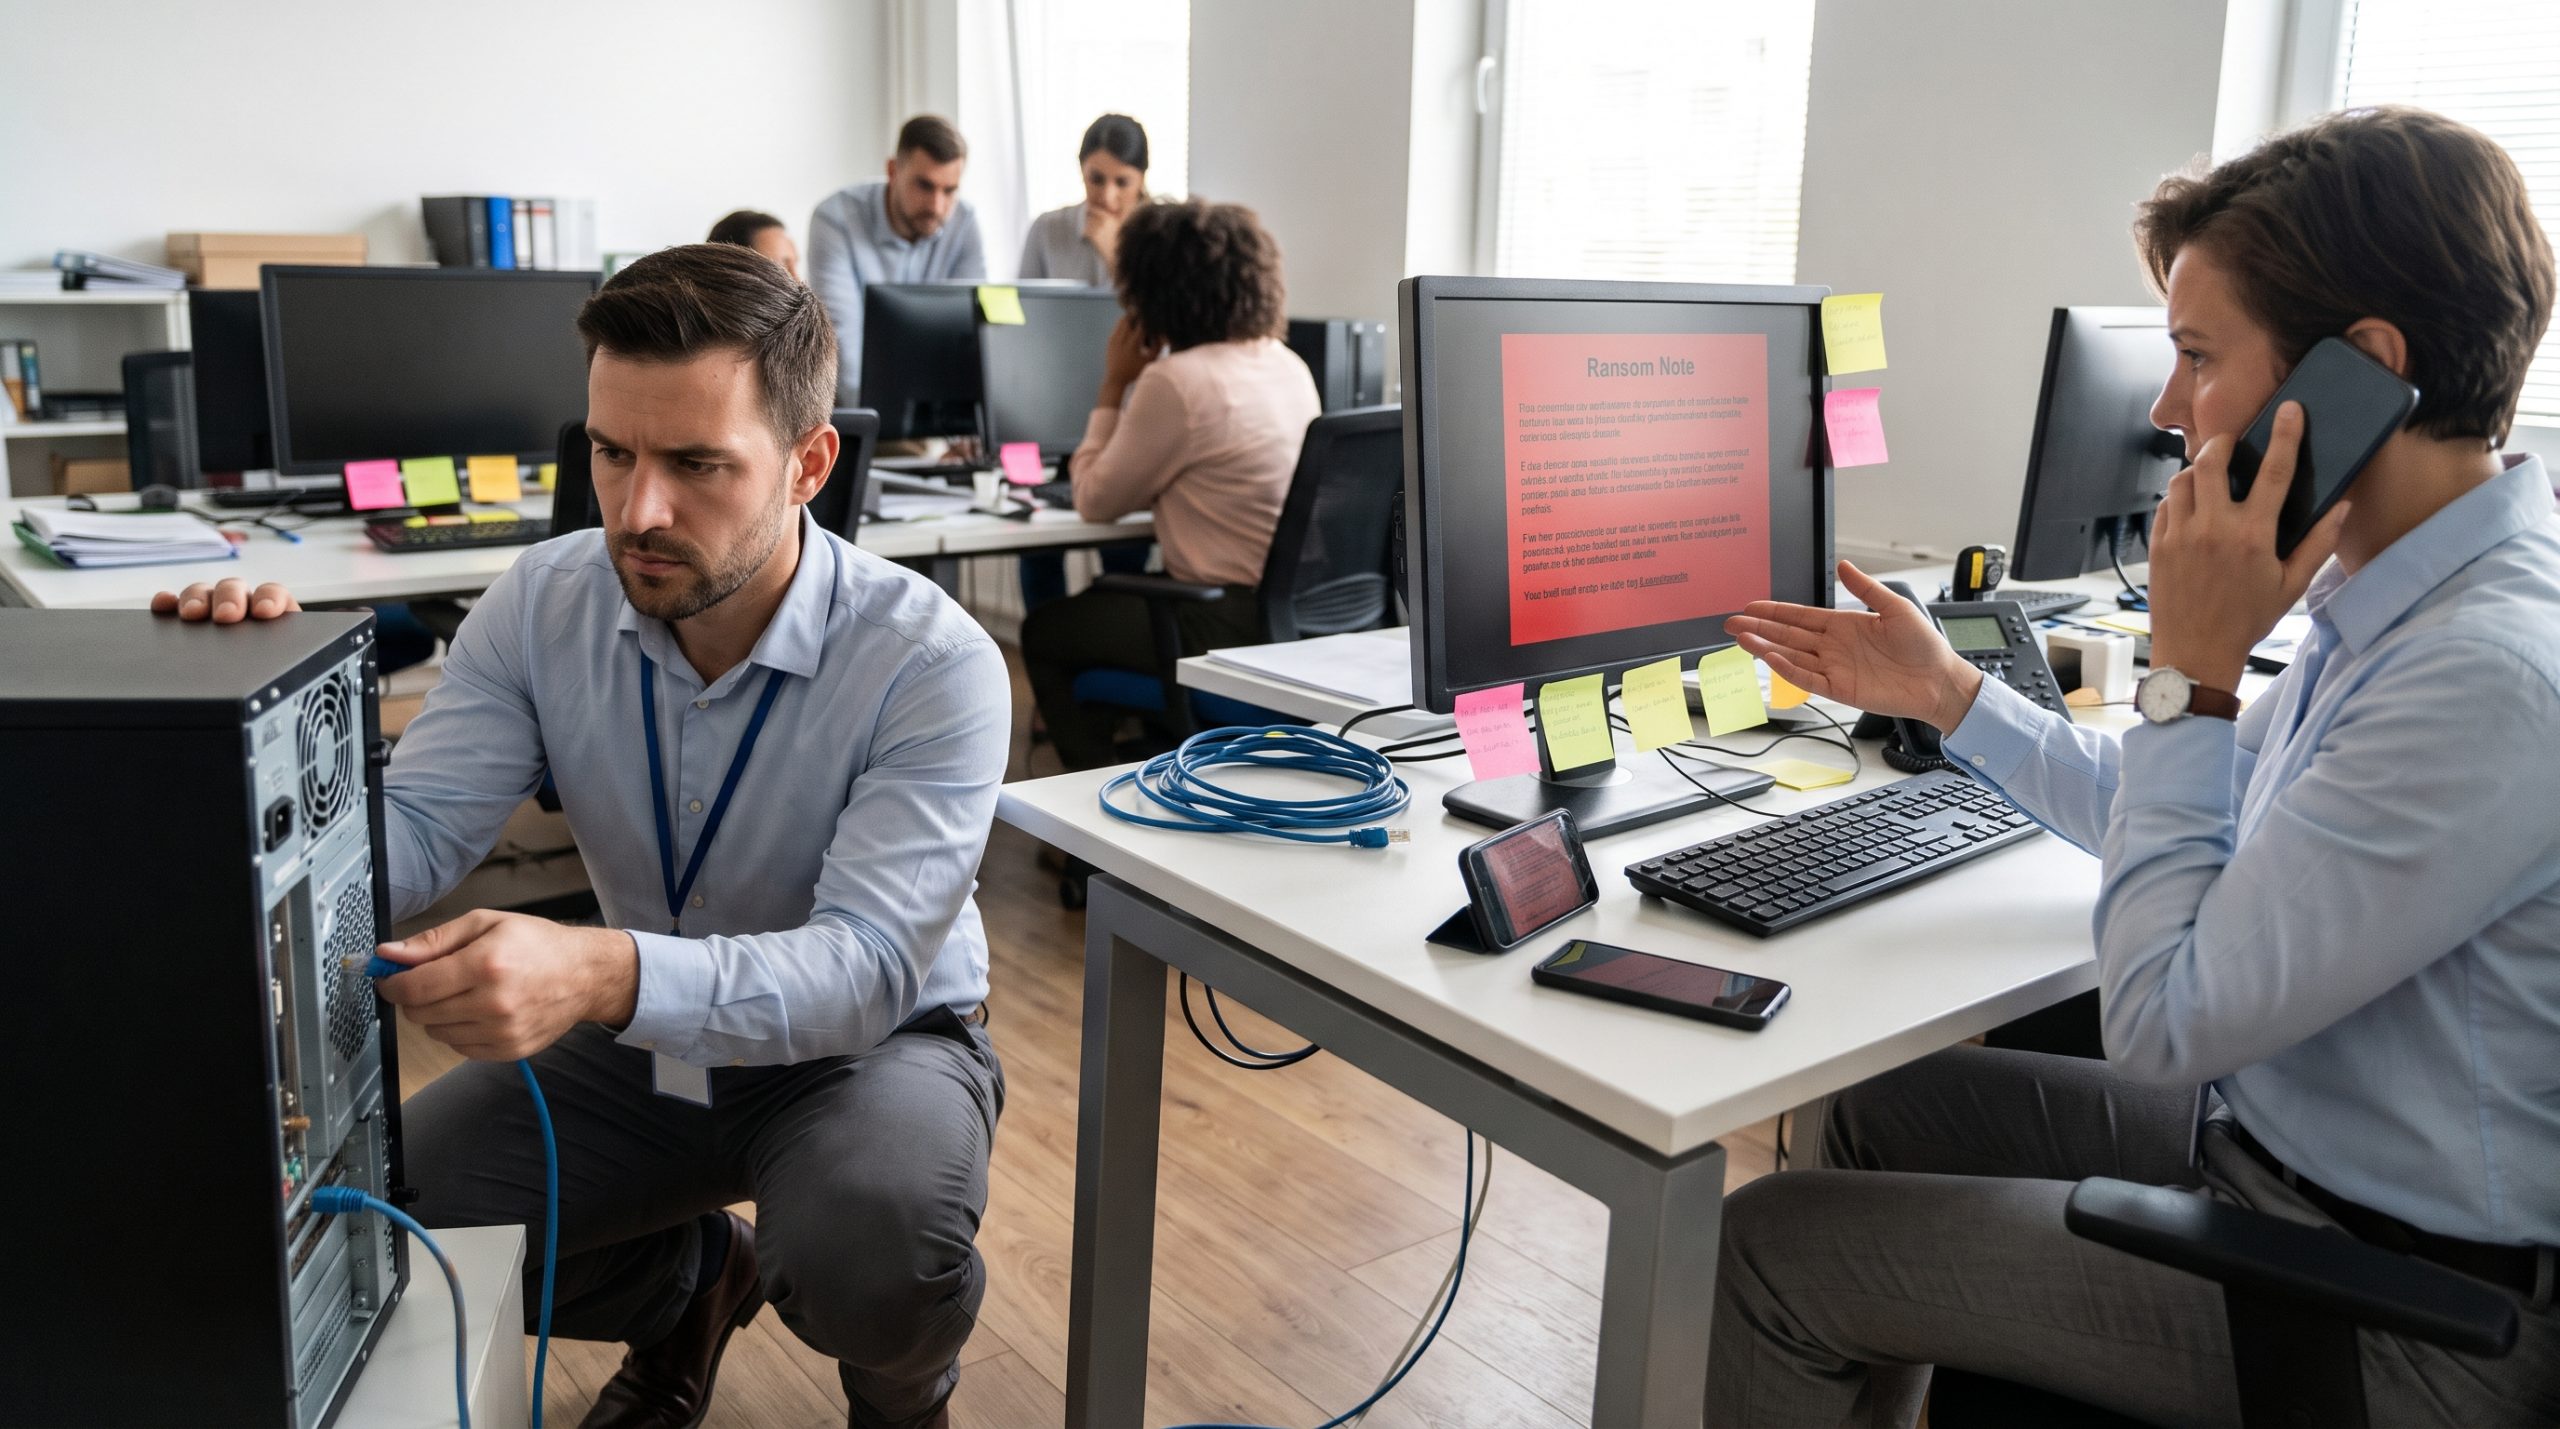
- Unplug the infected machines. Pull the network cable or turn off Wi-Fi. If several systems are hit, CISA advises taking the network offline at the switch level.
- Don’t power them off unless you have to. Shutting down wipes the memory, and that memory holds evidence investigators may need. Disconnect first, and power down only if you can’t isolate the machine any other way.
- Talk by phone, not email. If the attackers are still inside, they may be reading your inbox. Use phone calls or a separate channel so they don’t learn you’ve spotted them.
- Leave the ransom note alone. Take a photo of it. Don’t reply, and don’t click anything in it.
One more thing. Don’t start restoring yet. CISA’s guidance is to find out how the attackers got in before you rebuild, because some attacks leave an earlier piece of malware (a “dropper”) behind. Restore on top of that, and you’re back where you started.
Who to Call After a Ransomware Attack
More people than you’d think. It’s tempting to call your IT provider and stop there, but CISA’s checklist names a wider group, and some of them have deadlines.
- Your IT or managed security provider. They lead the hunt for how the attackers got in, and they handle the rebuild.
- Your cyber insurance carrier. Call early. Many policies have rules about which response firms you can use, and you’ll want to know them before you hire anyone.
- Federal law enforcement. Report it to CISA, your local FBI field office, or the FBI’s Internet Crime Complaint Center (IC3). CISA also suggests asking law enforcement whether a free decryptor exists for your strain.
- Your attorney, if customer or employee data may have been taken. Breach notification rules can kick in, and they come with their own deadlines.
Write things down as you go (what you saw and who you called). That timeline helps your insurer. It helps investigators too.
Should You Pay the Ransom?
The FBI says no. Its ransomware guidance gives two main reasons. Paying doesn’t guarantee you’ll get your data back, and it rewards the criminals, which pulls more of them into the business.
Plenty of companies pay anyway. In Sophos’s State of Ransomware 2025 survey of IT leaders in 17 countries, nearly half of victims paid. The median ransom demand was $1 million.
Here’s the part people miss. Paying doesn’t skip the cleanup. You still have to find the way in and rebuild clean systems. Every file you get back needs testing too. The attackers may also have copied your data before encrypting it (a tactic called double extortion), and a payment doesn’t make that copy go away.
Thinking about it anyway? That’s not a call to make alone. Bring in your attorney and your insurer before anyone talks to the attackers.
Restore From Backups and Rebuild Clean
This is where recovery actually happens. And it only goes smoothly if you have backups the attackers couldn’t reach.
Find the Way In First
First, detective work. Skip it, and you’re rebuilding with the back door still open.
Before anything goes back online, your IT team needs to know how the attackers got in. CISA’s checklist calls for hunting through logs for new or upgraded user accounts and odd VPN logins.
Remote-access tools nobody remembers installing are another giveaway. Attackers also go after backups and shadow copies (the restore points Windows keeps), so those get checked too.
Rebuild in Priority Order
Not everything comes back at once. CISA recommends a predefined list of critical systems (and what each one depends on), so the business-critical pieces return first. We’d take payroll over the conference room display every time.
Rebuilt machines should start from clean, standard images. Never the infected ones. Reset passwords for every affected account and patch whatever let the attackers in. Then a designated IT or security lead formally calls the incident over.
Restore Your Data
Now the backups. CISA’s guidance is to restore from offline, encrypted backups in priority order, and to let only clean systems back onto the network.
That word “offline” matters. A backup drive that stays plugged into the network can get encrypted right along with everything else. It’s why cloud backup services that keep copies separate from your network are such a big part of ransomware planning. Backups held up for 54% of victims in Sophos’s 2025 survey. That was the lowest share in six years.
How Long Does Ransomware Recovery Take?
Longer than the attack itself, almost always. Encryption can happen overnight. Getting back to normal is measured in days or weeks.
There’s some good news. In Sophos’s State of Ransomware 2025, more than half of organizations recovered within a week. The same survey found average recovery costs fell to $1.53 million, down from $2.73 million the year before.
Recovery cost is a lot more than a ransom. It’s downtime, lost orders, staff overtime, and the outside help needed to rebuild. What keeps it down? Clean backups you can actually restore, and a written ransomware response plan your team has practiced before they need it.
How to Keep It From Happening Again
The last step on CISA’s list is easy to skip: write down what you learned and update your plans. Don’t skip it. Attackers who got in once know the way back.
- Fix the way in. Whatever the attackers used (a stolen password or an unpatched server, say) needs to be closed for good.
- Test your backups. Keep at least one copy offline or isolated from the network. A backup you’ve never restored is a guess, not a plan. Our post on why backup and disaster recovery solutions are essential covers what a solid setup looks like.
- Turn on multi-factor authentication everywhere it’s offered, starting with email and remote access.
- Write a ransomware response plan. List your critical systems in recovery order, and put phone numbers on paper (your IT provider and your insurer, at minimum). Your contact list won’t help if it’s stuck on an encrypted server.
Not sure where you stand today? A cybersecurity assessment shows where your backups and staff habits leave room for an attack.
Frequently Asked Questions
What is ransomware recovery?
The work of getting a business back up after ransomware encrypts its systems. That means containing the attack and finding how the attackers got in. It also means rebuilding clean machines and restoring data from backups. Paying the ransom isn’t recovery, because you still have to do all of that cleanup afterward.
How do companies recover from ransomware?
Most follow a sequence close to CISA’s: isolate infected systems, report the attack, hunt down how the attackers got in, rebuild clean machines, then restore data from offline backups. In Sophos’s 2025 survey, 54% of victims recovered data from backups. Nearly half paid a ransom.
How long does it take to recover from ransomware?
Days to weeks for most businesses. Sophos found more than half of organizations recovered within a week in 2025. Missing backups or a slow start on containment can stretch that out.
Can I recover files from a ransomware attack?
Often, yes. The best route is restoring from a clean backup that the attackers couldn’t reach. If you don’t have one, ask law enforcement whether a free decryptor exists for your strain, which CISA recommends. Stick to tools law enforcement or your IT provider points you to.
How much does ransomware recovery cost?
More than most expect. Sophos put the 2025 average at $1.53 million, down from $2.73 million the year before. Downtime and outside help are what drive it.
How should you respond to a ransomware attack?
Fast, and in the right order. Disconnect the infected machines from the network right away, but don’t power them off unless you have to. Then call your IT provider and your cyber insurer.
Report the attack to CISA or the FBI, and hold off on restoring anything until you know how the attackers got in. If the cleanup can’t start right away, CISA suggests imaging the affected systems and saving logs and malware samples, so investigators have something to work with later.
What is a ransomware recovery plan?
A written playbook for the day ransomware hits. A good one lists your critical systems in the order they need to come back, plus where clean backups live and how to restore them. Keep printed contact numbers for your IT provider and your insurer in it too. It should be tested before you need it. A plan nobody has practiced tends to fall apart the moment the servers go dark.
What is a double extortion ransomware attack?
Two threats in one attack. The criminals encrypt your files and also copy your data before they do it. Then they threaten to leak it unless you pay. Restoring from backups fixes the encryption, but it doesn’t undo the theft.
How do you detect a ransomware attack?
Sometimes the first sign is a ransom note. Earlier clues include new admin accounts nobody created and VPN logins at odd hours. Security software that watches endpoints and logs can flag that activity before encryption starts.
How do you prevent a ransomware attack?
Layers. Patch your systems and turn on multi-factor authentication, especially for email and remote access. Keep tested backups offline, and train staff to spot phishing emails.
Get Help Before You Need It
Ransomware recovery is a race you’d rather not run. It goes a lot faster when the backups and the plan are in place before the attack, not after.
Function4’s cybersecurity services help businesses get ready for exactly this, and we can review your backups and response plan with you. Want to talk it through? Contact Function4, and we’ll set up a time with our team.
